
Dashboard JWTs and external API keys are not interchangeable. Use the authentication method documented for the endpoint you are calling.
Open the Valuez dashboard
The production dashboard is available at dashboard.valuez.ai.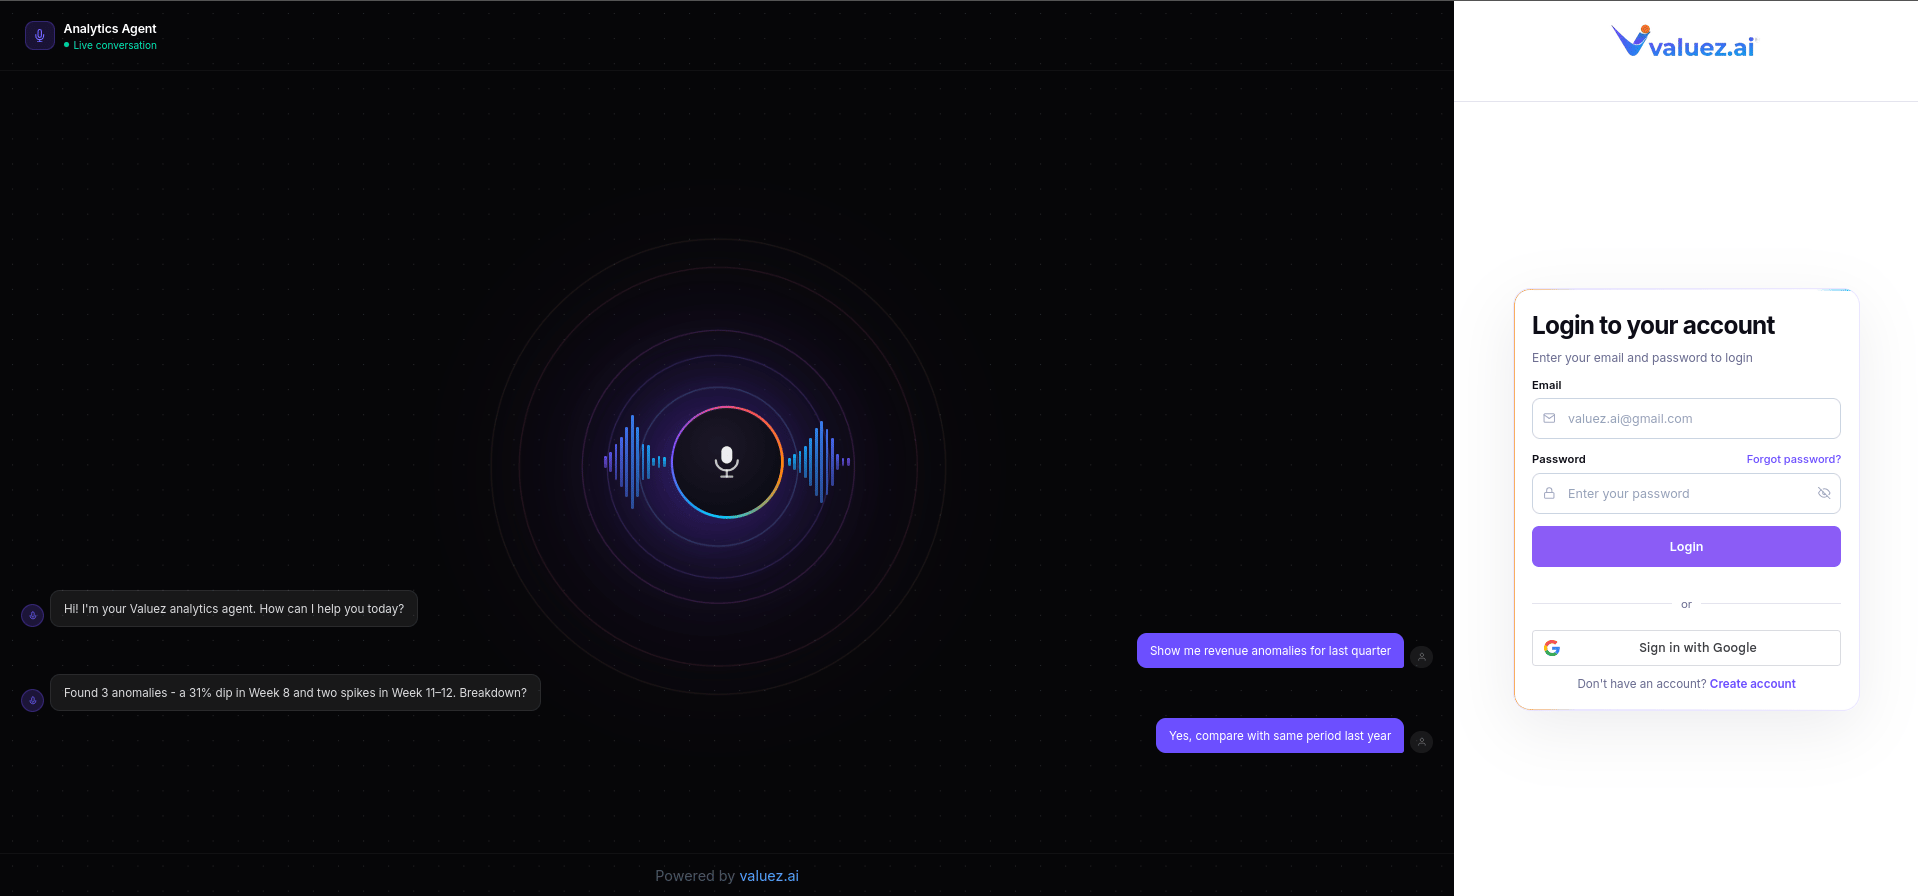
Valuez AI login screen
Log in with email and password
1
Open the login page
Visit dashboard.valuez.ai and confirm that you are on the official HTTPS domain.
2
Enter your registered email
Enter the email address associated with your Valuez account or team invitation.
3
Enter your password
Enter your password. Use the eye control to show or hide the value while typing.
4
Select Login
Valuez validates the credentials and checks that the account is active and email verification requirements are satisfied.
5
Access the workspace
After successful login, the dashboard loads your user profile, organization access, subscription entitlement, and module permissions.
Log in with Google
The login page includes Sign in with Google and supports Google’s One Tap login experience where available.1
Choose Sign in with Google
Select the Google button and choose the Google account whose email address should be associated with Valuez.
2
Complete Google verification
Google returns a signed identity token. The Valuez backend verifies that token using the configured Google client ID.
3
Complete account setup when requested
A new Google user may be asked to provide an organization name, a 10-digit phone number, and a Valuez password before signup is completed.
4
Enter the dashboard
After successful authentication, Valuez creates its own application session and loads your authorized workspace.
Google authentication verifies your Google identity, but Valuez still applies its own account status, workspace membership, plan entitlement, and permission checks.
Create an account
You can register with the Valuez signup form or use Sign up with Google.Email registration
The standard registration flow collects your name, email address, organization, phone information, password, and other business details required by the form. You must accept the displayed terms before creating the account. The backend requires:- a valid email address;
- an organization name between 2 and 100 characters;
- a password between 8 and 25 characters;
- a name between 2 and 50 characters;
- valid invitation identifiers when registration is opened from an invitation.
Google registration
Google signup verifies the Google identity first. If the account is new, Valuez displays Complete your account and requests the remaining workspace information. The current signup interface asks for:
The interface advises using uppercase, lowercase, number, and special-character combinations for a stronger password.
Verify your email address
Email-and-password accounts may be prevented from logging in until verification is complete.1
Open the verification message
Find the Valuez verification email sent after registration.
2
Select the verification link
The link calls the keyed email-verification endpoint and activates the verified state for the account.
3
Return to login
Sign in with the verified email address and password.
Reset or create a password
Forgot password
Use Forgot Password and enter the registered email address. Valuez sends a keyed password-reset link. Open the link and choose a new password between 8 and 25 characters.Google account password setup
If an account was created through Google and does not yet have a Valuez password, an email/password login attempt can offer to send a password-setup email. After setting a password, the user can continue using Google or use email and password.Change password
Authenticated users can change their password through the profile or password workflow available in the dashboard. After a suspected compromise, change the password and rotate any exposed API keys.Dashboard session authentication
After a successful login, Valuez returns an application JWT. The frontend sends it to protected dashboard APIs using the bearer scheme:- The token signature and expiration.
- The user identifier contained in the token.
- That the user account still exists.
- That the account is active.
- The requested organization membership.
- The plan and platform entitlement.
- The permission required by the requested route.
Workspace and organization access
Users can belong to one or more organizations. When a specific organization is selected, requests can include:Roles and permissions
Authentication confirms identity; permissions determine allowed actions. Valuez modules can distinguish actions such as:- view;
- create;
- edit;
- delete;
- upload;
- download;
- payment.
Device access and IMEI rules
Some mobile or team workflows can provide an IMEI or device identifier during login. When device locking is enabled for that account, the first valid device can become the registered device. A login from another device can be rejected until an authorized administrator resets the stored device identifier. This behavior does not normally affect browser login when no IMEI is supplied.External API authentication
External agent and speech APIs use an API key rather than the dashboard bearer token:API key types
Generate these keys from APIs and Integrations in the dashboard. See API Keys and Integrations.
API base URL
The production API base URL shown in the existing Valuez documentation is:External API request example
Security features
Security best practices
Use Google or a strong unique password
Use Google or a strong unique password
Do not reuse a password from another service. For password accounts, use the supported 8-to-25-character range and include uppercase, lowercase, numeric, and special characters.
Never expose dashboard tokens or API keys
Never expose dashboard tokens or API keys
Use dashboard JWTs only for authenticated sessions and API keys only from trusted server-side code. Never embed privileged credentials in browser JavaScript.
Store integration keys in environment variables or a secret manager
Store integration keys in environment variables or a secret manager
Keep secrets outside source control. Use separate values for development, staging, and production.
Create separate API keys for separate integrations
Create separate API keys for separate integrations
Separate keys limit the impact of compromise and make usage easier to audit.
Review workspace members regularly
Review workspace members regularly
Remove former users, review role changes, and restrict billing, recordings, integrations, and invitation permissions.
Rotate credentials after exposure
Rotate credentials after exposure
Revoke or delete the exposed integration, issue a new key, update the authorized client, and review API history for misuse.
Troubleshooting
Next steps
API Keys and Endpoints
Review external agent and speech authentication with request examples.
Dashboard Overview
Understand the major Valuez dashboard areas.
Integrations
Create API keys and configure external services.
Agents
Create and configure an AI voice agent.